
Beyond Passwords: Biometrics, Passkeys and the New Shape of Account Security
Long‑used character strings are quietly giving way to sign‑in experiences built around the person, not the code they remember. Phones, laptops, and browsers now coordinate to prove who is present, tying access to physical traits or unlocked devices instead of fragile, guessable secrets.
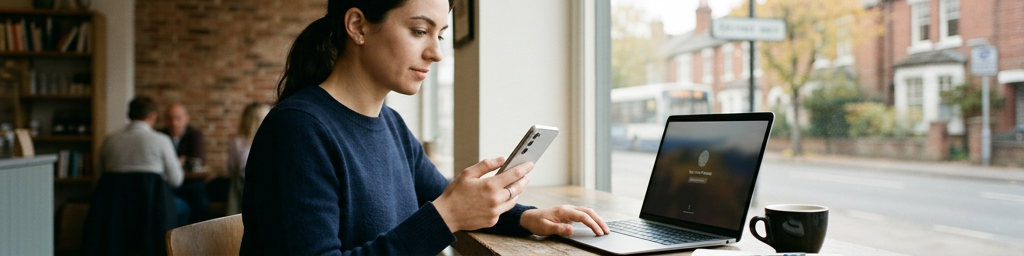
This story is part of Esgamesol's practical reading library across everyday topics.
Why traditional logins are reaching their limits
The problem with secrets people have to remember
Character‑based logins were built for a world with fewer sites, fewer devices, and far less automation. Today, people in everyday digital life juggle dozens of accounts across phones, laptops, and shared screens. Faced with that overload, many fall back on the same handful of easy‑to‑type strings or predictable patterns. Attackers exploit this by trying stolen combinations across multiple services, turning one leak into many break‑ins. Even strong choices can be captured through convincing fake pages and scam emails that lure people into typing real credentials into the wrong place. Meanwhile, support teams spend large amounts of time unlocking accounts, handling resets, and calming understandably frustrated users.
Why attackers love reusable credentials
From an attacker’s point of view, a world full of guessable, reusable secrets is ideal. Large lists of stolen login details circulate openly, feeding automated tools that test combinations at scale until something works. Once one account falls, similar secrets are tried elsewhere, often with success. Phishing tricks remain effective because any page that looks believable enough can collect the same characters that work on the real site. Even additional steps like texted codes can sometimes be hijacked, especially when people are rushed or pressured. The imbalance is clear: attackers only need to succeed occasionally, while defenders have to block every angle, every time.
How device‑based sign‑in actually works
From “what you know” to “what you hold”
Modern sign‑in flows are shifting away from shared secrets and toward unique cryptographic keys anchored to personal devices. Instead of sending a password across the network, a service stores a public identifier, while the matching private element remains in secure hardware on a phone, tablet, or computer. When access is requested, the service sends a one‑time challenge. The device signs that challenge using its private key and returns the result. If the signature checks out against the stored public value, entry is granted. No reusable secret moves over the wire, and nothing on the server can be reversed to impersonate the user elsewhere.
Local checks: biometrics and device unlocks
Of course, the device itself must not be an open door. That is where screen locks, local PINs, and biometric checks come in. Before using its private key, the device asks for proof that the right person is present: a fingerprint, a face match, or a short PIN only the owner should know. This verification happens entirely on the device, never on the remote service. The online system simply sees that a valid cryptographic response came from a trusted device that has passed its own internal checks. The user experiences a single, quick action, but under the surface multiple layers of assurance are working together.
Passkeys in everyday life
What these new digital keys really are
Passkeys are a friendly wrapper around public‑key cryptography designed for normal consumers, not specialists. Each one is created for a specific service and account, generating a pair of linked keys. The public half lives on the service’s side; the private half never leaves the person’s device. Signing in becomes a matter of proving control of that private half, usually triggered by a familiar system prompt. Because every site gets its own unique pair, there is nothing to “reuse” between services, and leaks of stored public information do not open doors elsewhere.
Why they resist phishing and large‑scale theft
Look‑alike pages and misleading links work by capturing what people type. Passkey‑based flows dramatically reduce this avenue. The device checks which site is requesting authentication and will not complete the process for a mismatched domain. There is no box to fill with a secret string that can be tried later. Attackers cannot simply copy a database of hashes and run offline guessing games, because there is no shared password to recover. Stealing access now requires physical control of a device plus whatever local check protects its keys, raising the cost and difficulty of abuse.
Multi‑device use without spreading secrets
In real life, people bounce between multiple screens. Well‑designed passkey systems support that by letting someone register several devices for the same account or, in some ecosystems, synchronize keys within an encrypted cloud tied to a broader platform identity. A new phone or laptop can be enrolled by proving control of an existing device or recovery method. In some cases, a phone can temporarily act as the authenticator for a shared computer: scan a QR code, approve on the handset, and the browser session opens without copying any long‑term secret to that computer.
| Scenario type | How passkeys typically help | Things users should keep in mind |
|---|---|---|
| Personal daily accounts | Faster sign‑ins on phones and laptops with fewer lockouts | Ensure device backups and recovery methods are in place |
| Work tools and email | Stronger protection against targeted phishing and reuse | Follow organization guidance on registering trusted devices |
| Shared or public devices | Temporary sessions triggered from a phone rather than typing | Always sign out and avoid storing keys on shared hardware |
Passkeys fit naturally into these situations, giving more protection with fewer repeated steps, as long as people understand how to enroll devices and keep recovery options current.
Biometrics and privacy‑conscious verification
How fingerprints and faces fit into the picture
Fingerprint readers and facial recognition features act as convenient gatekeepers for sensitive actions. When a sign‑in prompt appears, touching a sensor or looking at the camera triggers a local comparison against a stored template. If there is a match, the device is willing to use its private key for the waiting challenge. The remote service never needs a copy of the fingerprint or face; it only needs the signed response. From the user’s point of view, the same gesture they use to unlock their screen now confirms access to critical accounts as well.
Where biometric data actually lives
Many concerns around this model center on privacy. On modern hardware, biometric templates are normally stored inside dedicated secure components, separate from general storage. These components expose only simple answers—match or no match—to the main operating system. Templates themselves are mathematical representations rather than raw images, and are not meant to leave the device. Even if an online service suffers a breach, those templates are not among the exposed material, because they were never uploaded in the first place. If preferences change, biometrics can often be disabled at the device level, falling back to local PINs.
Balancing convenience, risk, and inclusivity
Biometric checks feel almost effortless compared with typing long secrets, especially for people who regularly unlock their devices dozens of times a day. That ease encourages consistent locking, which protects keys when devices are lost or stolen. At the same time, not everyone can or wants to use biometric traits. Good implementations always include alternatives: PINs, patterns, or hardware tokens that provide access without requiring physical characteristics. Additional steps—such as second devices or recovery codes—can be required for especially sensitive actions, ensuring that convenience does not override caution.
Why organizations are embracing these models
Security gains that matter in practice
For security teams, device‑bound keys reduce some of the most common failure points. There is no central password database full of secrets that can be reused, and large phishing campaigns become less rewarding when there is no password field to harvest. Automated credential stuffing attacks have little to work with, since each key is bound to a specific service and device. Even if an attacker tricks someone into visiting a fake page, the device itself is less likely to approve a key operation for the wrong destination.
Better experiences for staff and customers
People in English‑speaking markets are now used to tapping a fingerprint to pay, unlock, or confirm. Extending that to workplace tools, banking, and consumer apps makes sign‑in feel consistent across contexts. Fewer forgotten secrets mean fewer support contacts and less downtime. Customers are less likely to abandon a registration when they can simply confirm on a phone instead of creating and later recalling a complex string. Internally, staff can move between tools under a single, strong session, reducing repetitive prompts without lowering safeguards.
| Use case focus | Benefits of moving away from passwords | Practical considerations |
|---|---|---|
| Employee access | Fewer reset tickets, smoother single sign‑on experiences | Clear onboarding, device replacement and recovery paths |
| Consumer services | Reduced account takeover risk, quicker sign‑ups | Simple explanations of new flows and backup options |
| High‑sensitivity apps | Strong defense against targeted attacks | Extra checks for admin or financial actions |
These gains depend on thoughtful rollout, testing with existing systems, and transparent communication so that people know what to expect and how to recover if something goes wrong.
Planning a realistic transition
Completely removing passwords overnight is rarely possible. Many services begin by offering new sign‑in options alongside existing ones, then gradually encouraging the safer path. Some older applications or devices might remain on legacy methods until they can be updated or retired. Throughout this period, organizations need clear policies for lost devices, backup authenticators, and emergency access. Training, support documentation, and small pilot groups help iron out issues before wider expansion. Over time, as more people rely on device‑centric keys, the role of passwords can shrink to a minimal safety net.
Q&A
-
How do biometric login methods improve security compared to traditional passwords?
Biometric logins tie access to unique physical traits, making credentials harder to steal, reuse, or share. They also reduce phishing and credential stuffing risks, while improving user convenience and lowering password reset support costs. -
What makes modern passkey security standards resistant to phishing attacks?
Passkeys use public-key cryptography bound to specific domains, so credentials never leave the device and can’t be typed or read by attackers. Even if a user clicks a fake link, the passkey simply won’t work on the fraudulent site. -
How can multi-device access control be implemented without sacrificing user experience?
Organizations can combine device binding, risk-based authentication, and session continuity, allowing trusted devices seamless access while challenging new or high-risk devices with step-up verification, keeping flows smooth yet secure. -
What role do identity verification tools play before enabling secure user authentication?
Identity verification tools confirm a user is who they claim to be—via document checks, liveness detection, and database validation—before issuing credentials, reducing synthetic identity fraud and strengthening downstream authentication trust. -
Which account protection technologies best complement secure user authentication in high-risk environments?
Combining strong authentication with device fingerprinting, behavioral analytics, real-time threat intelligence, and adaptive access policies enables dynamic responses to suspicious activity, like extra verification or temporary blocks.